
Blog
Palo Alto - Cortex - Extended Security Orchestration, Automation and Response (XSOAR)
14 October 2024 · Updated 15 September 2026
Palo Alto Cortex - Extended Security Orchestration, Automation and Response (XSOAR)
What is XSOAR?
Security orchestration, automation and response (SOAR) technology helps coordinate, carry out and automate tasks across different people and tools on a single platform. This allows organizations not only to respond quickly to cyber security attacks, but also to observe, understand and prevent future incidents — and so improve their overall security posture.
XSOAR is the machine-based execution of security actions with the power to detect, investigate and remediate cyber threats without manual human intervention. It handles most of the routine work for the SOC team, so they no longer have to triage every alert as it arrives and deal with it by hand. Security automation can:
. Detect threats in your environment.
. Triage potential threats into three stages.
. Determine whether action should be taken on the incident.
. Contain and resolve the problem.
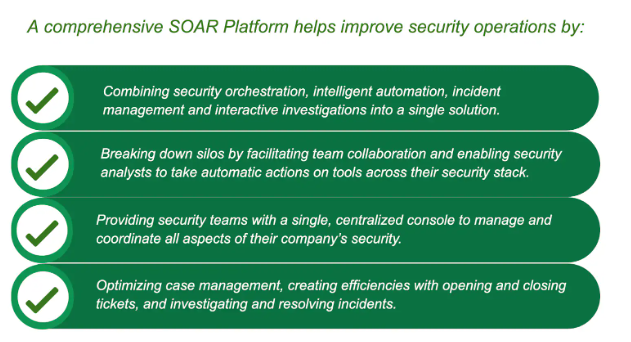
All of this can happen within seconds without any intervention from human staff. Security analysts no longer need to follow the steps, instructions and decision-making workflow required to investigate an incident and determine whether it is genuine. Repetitive, time-consuming actions are taken off their hands, so they can focus on more important, value-adding work.
SOAR platforms take in alert data, and those alerts then trigger playbooks that automate and orchestrate response workflows or tasks. Using a combination of human and machine learning, organizations can then analyse this varied data in order to understand and prioritize automated incident response actions against future threats, creating a more efficient and effective approach to cyber security and to improving security operations.
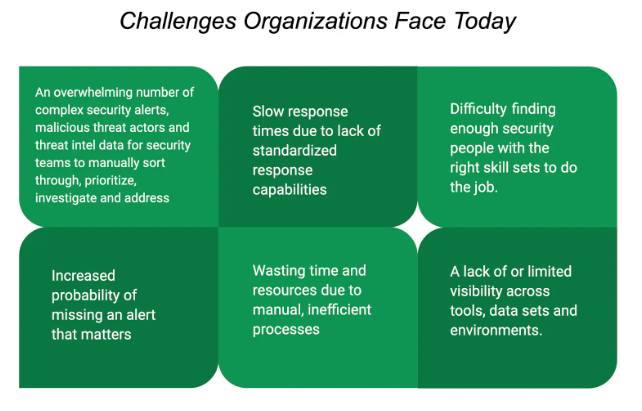
SOAR lets you:
See everything in one place. Your security team gains access to a single console that provides all the information they need to investigate and remediate incidents. Security teams can go to one place for the information they need.
Accelerate incident response. SOAR platforms have been shown to reduce both mean time to detect (MTTD) and mean time to respond (MTTR). Because many actions are automated, a large percentage of incidents can be handled instantly and automatically.
Avoid time-consuming actions. SOAR greatly reduces the false positives, repetitive tasks and manual processes that take up security analysts' time.
Access better intelligence. SOAR solutions aggregate and validate data from threat intelligence platforms, firewalls, intrusion detection systems, SIEMs and other technologies, giving your security team more insight and context. That makes it easier to resolve issues and improve practices. Analysts can conduct deeper and broader investigations when problems arise.
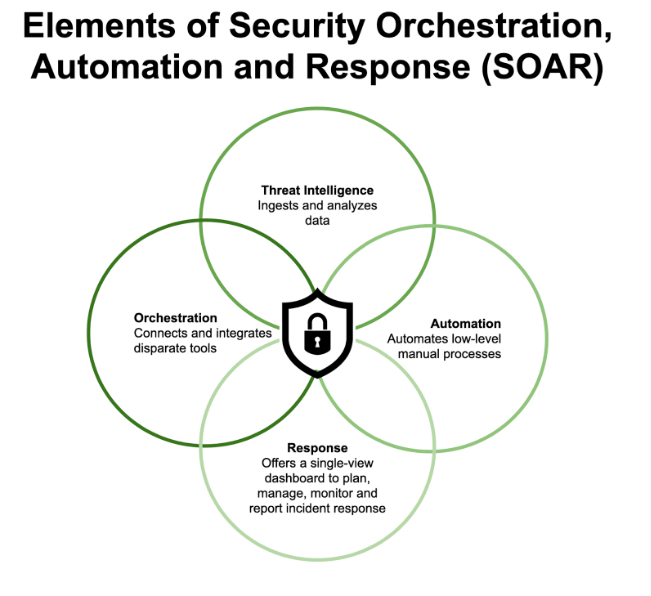
Improve reporting and communication. With all security operations activity gathered in one place and displayed on intuitive dashboards, stakeholders can get all the information they need, including clear metrics that help them identify how to improve workflows and reduce response times.
Improve decision-making. SOAR platforms aim to be user-friendly even for less experienced security analysts, offering features such as pre-built playbooks, drag-and-drop functionality for building playbooks from scratch, and automatic alert prioritization. A SOAR tool can also gather data and provide insights that make it easier for analysts to assess incidents and take the right actions to remediate them.