
Blog
A New Era in Network Security: Meet the S3M Security NAC Solution
13 August 2024
Network access control (NAC) has become one of the most critical elements of corporate security in a world where digitalization advances by the day. Organizations have to manage steadily growing network traffic and an ever-larger number of connection points securely. Here, the S3M Security NAC (Network Access Control) solution offers an innovative and effective approach to taking your security to the highest level.
Far from complicated, S3M Security is designed to integrate easily with your core network devices, in an effort to simplify network security processes and make them easy to understand.
It maintains an inventory of APNs, VPNs, gateways and firewalls. It also collects inventories of corporate devices, BYOD devices, and headless or IoT devices.
Authentication module: third-party database integration
S3M places great importance on integration, and its Network Single Sign-On module includes integration with Forti, Checkpoint, Palo Alto and Sophos firewalls. The Network SSO module passes user information to the firewall.
Network Single Sign-On (Network SSO):
The Network SSO architecture communicates effectively with every authenticated user to keep information flowing. After authentication it also allows data to be shared with other identity sources.
Hotspot module:
A customizable Layer 3 external captive portal
The Hotspot module has a fully customizable Layer 3 external captive portal that improves both user experience and security. It includes functions such as downloadable ACL, change of authorization and dynamic authorization. What matters here is its external capability: it is compatible with every enterprise-grade vendor.
When S3M Security encounters a vendor that is not in its records or included by default, it can add it to the system manually using the vendor's guides. It does not require an external log system for traffic logs, but it can also integrate with SIEM and SOAR systems for those who prefer them.
Endpoint protection (EPP):
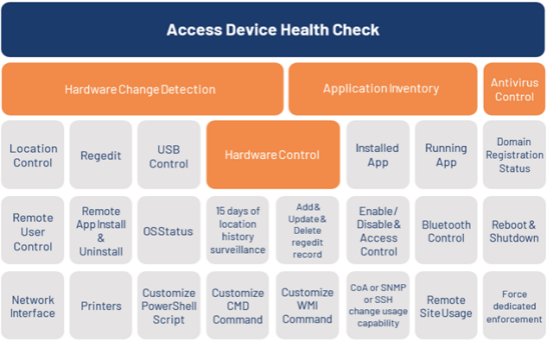
It has its own VPN infrastructure for establishing a secure connection. It offers ease of configuration with low hardware requirements. Use a single console to control the entire system.
What is "EdgeBoX"?
EdgeBoX is a NAC virtual appliance technology managed by the EdgeBoX Console, which keeps corporate data at the edge and allows every service to run at the edge. It can serve from 100 users up to 5,000 users.
It connects to the Console through its own VPN infrastructure. Over that secure connection, EdgeBoX applies the configurations it receives from the Console. It has no management interface of its own; operations are carried out from the L3 external captive portal web interface.
With low hardware requirements and configuration settings that can be stored both locally and in the cloud, it provides information security along with ease of configuration.
S3M Security NAC carefully inspects every device, user and application that wants to connect to the network. Thanks to that inspection, only authorized devices can access the network, which heads off security breaches.
For organizations that want to build a strong security shield against the challenges digitalization brings, the S3M Security NAC solution is an ideal choice. With advanced access control, monitoring, reporting and compliance capabilities, S3M Security NAC takes your network security to the next level.
Control who accesses your network, close your security gaps and safeguard business continuity. Manage your network with confidence with S3M Security NAC.